
579/69 Thursday, October 22, 2026
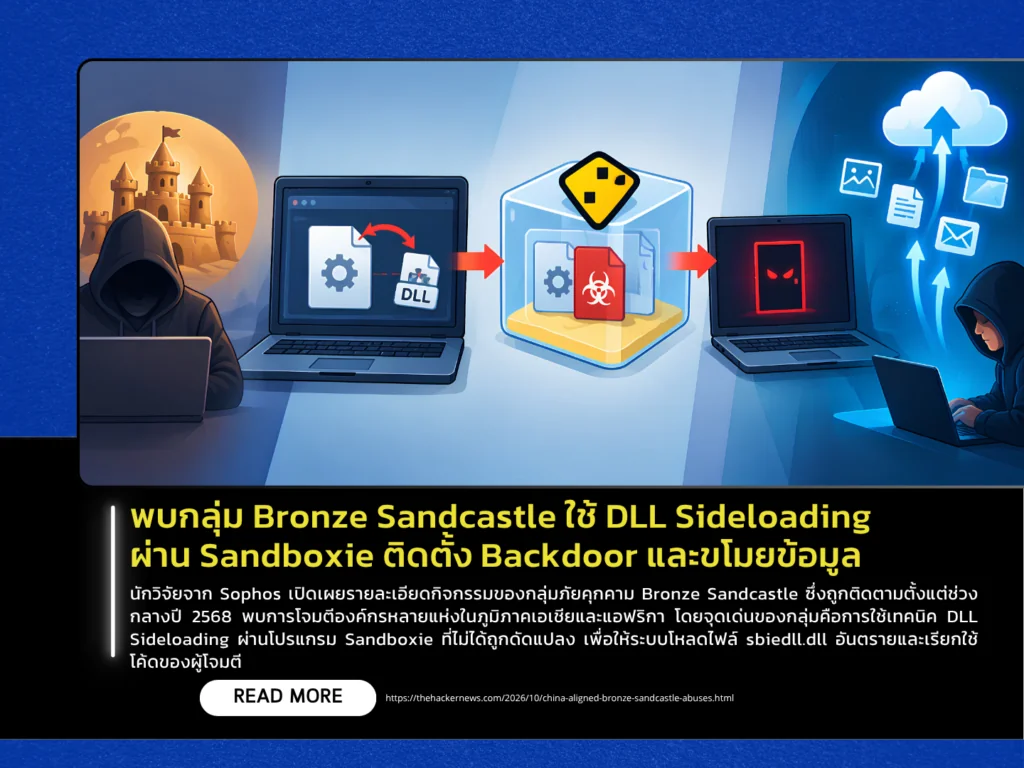
Researchers from Sophos have disclosed details of activity linked to the Bronze Sandcastle threat group, which has been tracked since mid-2025 and has targeted multiple organizations across Asia and Africa. A notable characteristic of the group’s activity is its use of DLL Sideloading through an unmodified version of Sandboxie, causing the system to load a malicious sbiedll.dll file and execute attacker-controlled code. Researchers also observed similar abuse involving other legitimate applications, including Java, Krita, NVDA, and Sysinternals tools. Sophos assessed that the activity is consistent with cyberespionage operations, although it has not been conclusively linked to any previously known threat group.
Once the malicious DLL is loaded, it decrypts a payload stored in the config.ini file and executes it directly from memory, reducing the likelihood of detection by conventional file-based scanning. The payload functions as a backdoor with a structure resembling Meterpreter and is capable of collecting system and user account information, enumerating processes and network data, recording keystrokes, capturing screenshots, and receiving additional commands from a Command-and-Control (C2) infrastructure. Researchers also found that some payload versions contacted GitHub and other commonly used online services to retrieve additional obfuscated configuration files.
Administrators should monitor for unusual execution of trusted applications alongside unknown DLL files, particularly involving Sandboxie and other applications identified in the report. They should also watch for behavior in which DLLs read local files before executing payloads directly from memory. Because Bronze Sandcastle uses obfuscated payloads and configuration data, signature-based detection or file scanning alone may not be sufficient. Organizations should therefore correlate endpoint and memory monitoring data with the Indicators of Compromise (IoCs) published by Sophos to help identify activity potentially associated with the campaign.
Source: https://thehackernews.com/2026/10/china-aligned-bronze-sandcastle-abuses.html