561/69 Monday, October 12, 2026
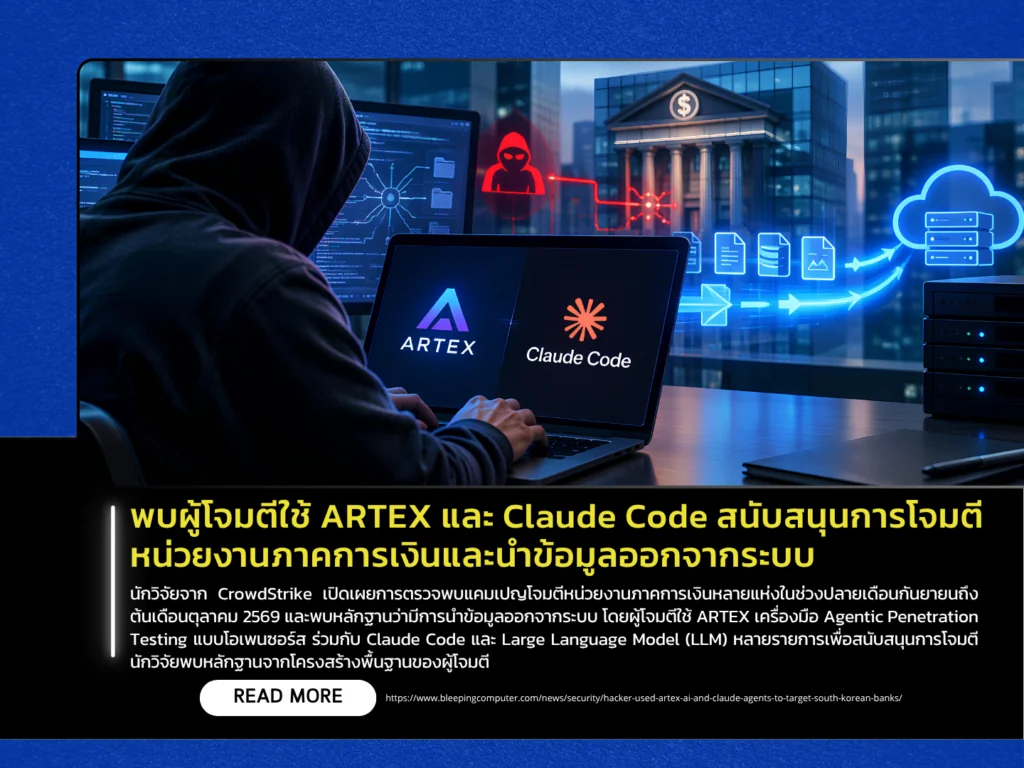
Researchers from CrowdStrike disclosed a campaign targeting multiple financial organizations from late September to early October 2026, with evidence indicating that data was exfiltrated from compromised systems. The attackers used ARTEX, an open-source agentic penetration testing tool, together with Claude Code and multiple Large Language Models (LLMs) to support their operations. Researchers identified evidence within attacker-controlled infrastructure, including Claude Code session histories, ARTEX configuration files, and Claude Memory data, linking the activity to attacks against several financial organizations. However, the exact number of affected organizations has not yet been confirmed.
The report stated that ARTEX was used as part of an automated penetration testing and attack workflow. The tool can assist with reconnaissance, vulnerability discovery, attack planning, and execution of security tools. The attackers also used Claude Code and other LLMs to support activities across related systems and infrastructure, while routing connections to targets through multiple proxy services. Researchers also observed searches for channels that could be used to publish or sell data obtained from the attacks. Based on the available evidence, the researchers assessed that the activity was likely financially motivated.
Organizations operating critical internet-facing services should review externally accessible systems and services, reassess authentication controls and access privileges, and examine logs for vulnerability scanning activity, unusual proxy usage, and outbound data transfers inconsistent with normal operations. If signs of compromise are identified, organizations should investigate the scope of accessed data, revoke affected sessions or credentials, and initiate incident response procedures promptly. The case demonstrates how agentic AI tools can help attackers accelerate and coordinate multi-stage attack activities.