
570/69 Monday, October 19, 2026
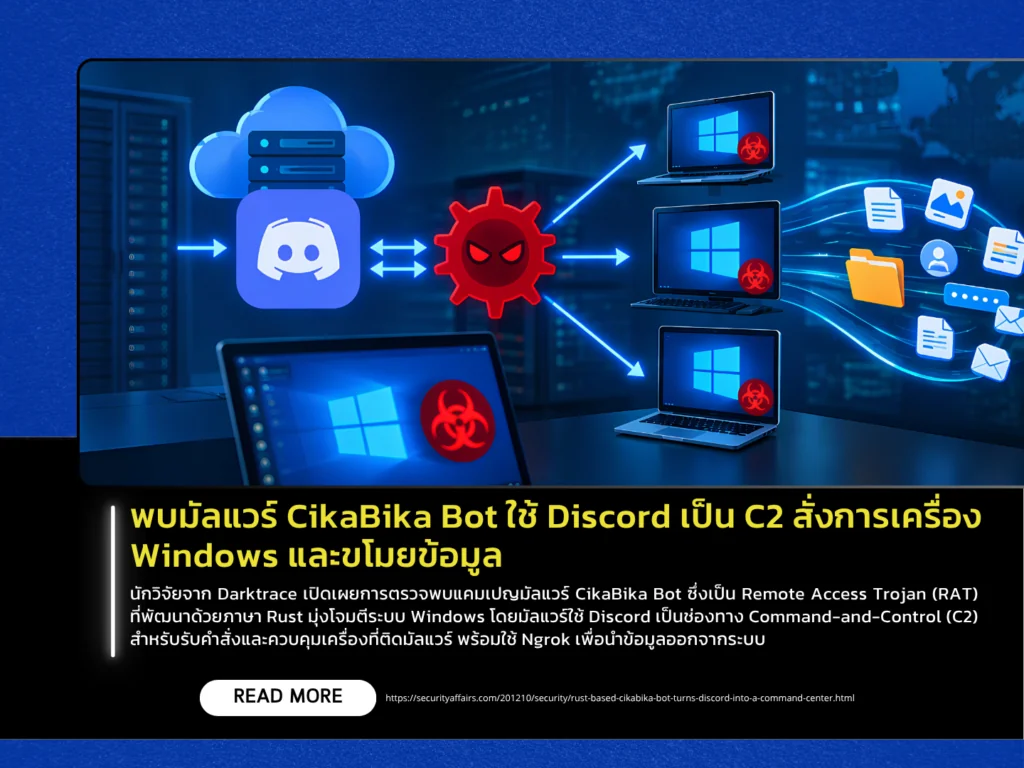
Researchers from Darktrace have disclosed a malware campaign involving CikaBika Bot, a Rust-based Remote Access Trojan (RAT) targeting Windows systems. The malware uses Discord as its Command-and-Control (C2) channel to receive commands and control infected machines, while Ngrok is used to exfiltrate data. The attack involves a disk image containing a PDF file intended to appear as a normal document and a Windows Shortcut (LNK) file disguised to resemble a Microsoft Word document. The delivery method used to send these files to victims has not yet been confirmed, although the attack artifacts are consistent with phishing activity.
When a user opens the LNK file, the system launches PowerShell without displaying a visible window to extract a payload embedded in the PDF file and execute a loader developed in Nim. The loader then extracts a Rust DLL and a PowerShell script to attempt malware installation through User Account Control (UAC) bypass and DLL Search-Order Hijacking using a Microsoft Edge directory. Researchers noted that the observed DLL does not contain all functions required by Edge, so it has not been confirmed that this method will succeed on every system. Once CikaBika is successfully executed, it collects system information, captures screenshots, and creates a separate Discord channel for each infected device, allowing attackers to execute commands, manage processes, transfer files, access the camera, and monitor on-screen activity.
Users should exercise caution with disk image files, shortcut files, or documents received from unverified sources, particularly files disguised as business documents that trigger PowerShell after being opened. Administrators should monitor for suspicious execution of PowerShell and computerdefaults.exe, as well as DLL files created in Microsoft Edge directories. They should also review connections to Discord and Ngrok that are inconsistent with normal organizational activity. However, connections to these services alone are not sufficient to confirm malware infection, as both can also be used for legitimate purposes.