
576/69 Wednesday, October 21, 2026
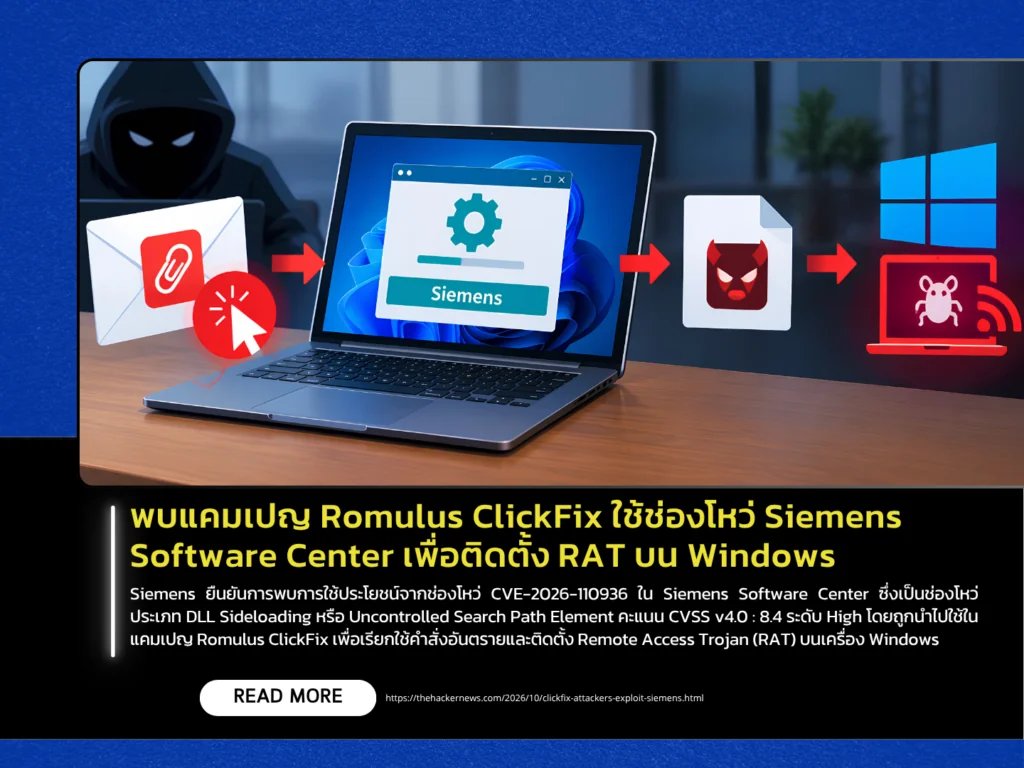
Siemens has confirmed exploitation of CVE-2026-110936 in Siemens Software Center, a DLL Sideloading or Uncontrolled Search Path Element vulnerability rated High with a CVSS v4.0 score of 8.4. The flaw has been used in the Romulus ClickFix campaign to execute malicious commands and install a Remote Access Trojan (RAT) on Windows systems. Siemens stated that the incident did not result from a compromise of its infrastructure or tampering with its official software update channel. Instead, attackers abused a legitimately signed copy of Siemens Software Center together with a malicious DLL specifically crafted for the attack.
The attack uses the ClickFix technique to trick users into copying and executing a command that launches PowerShell to download a malicious MSI file. The msiexec.exe process then runs AllMyBasic.msi, which contains an unmodified Siemens Software Center executable and an attacker-created archive.dll file. When the vulnerable version of the software is launched, it loads the DLL from a location that is not properly controlled, causing the malicious DLL to execute with the privileges of the application and leading to RAT deployment in the next stage. Exploitation of the vulnerability requires the attacker to already have local access to the system and the necessary privileges. In the observed campaign, attackers used ClickFix social engineering to persuade users to execute the commands required to initiate the attack chain.
Users should update Siemens Software Center to version 4.0.9.8 or later. Siemens stated that systems with the application already installed will automatically receive the update the next time the software is launched, and users should download software only through official Siemens channels. Administrators should investigate cases where SiemensSoftwareCenter.exe is executed from the AppData\Local\Programs directory through msiexec.exe, check for unknown DLL files located in the same directory as the application, and use the Indicators of Compromise (IoCs) published by Siemens as part of their investigation.
Source: https://thehackernews.com/2026/10/clickfix-attackers-exploit-siemens.html