
541/69 Friday, October 2, 2026
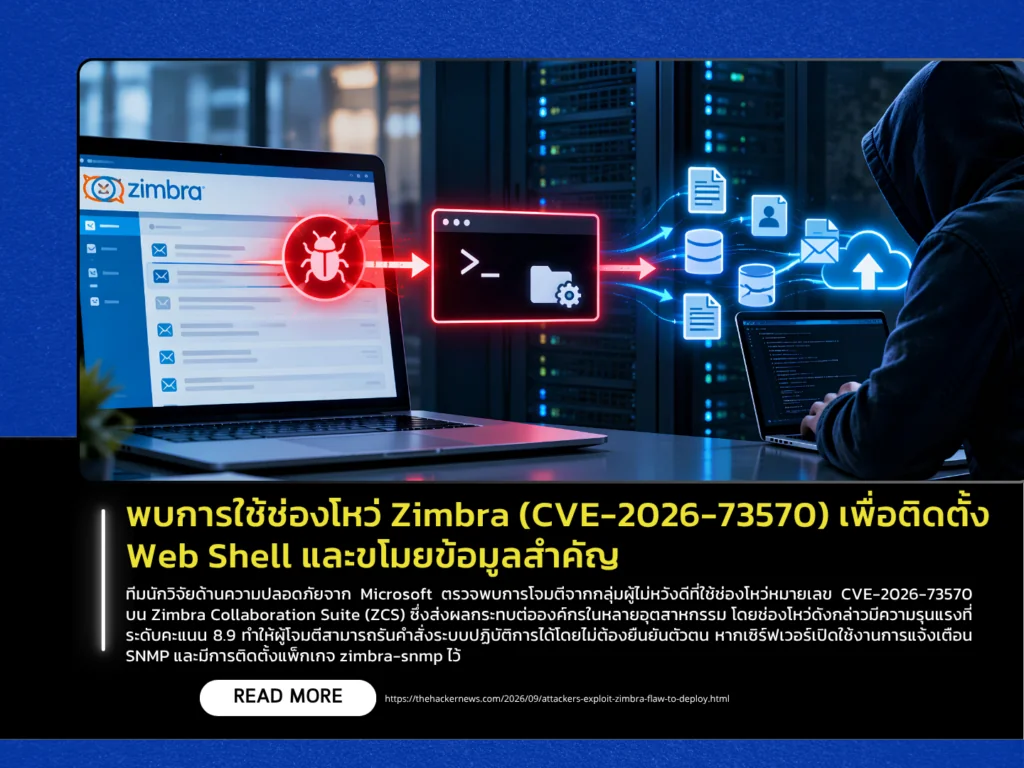
Security researchers from Microsoft have detected attacks exploiting CVE-2026-73570 in Zimbra Collaboration Suite (ZCS), affecting organizations across multiple industries. The vulnerability has a severity score of 8.9 and can allow unauthenticated attackers to execute operating system commands when the server has SNMP notifications enabled and the zimbra-snmp package installed. The issue was initially reported by CERT Polska, and CISA later added the vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, urging organizations to apply updates promptly to mitigate the threat.
The observed attacks followed a structured sequence. Attackers first exploited the vulnerability to inject commands through SNMP notifications and execute malicious payloads. They then established long-term persistence through service configurations, startup files, and SSH keys, while also escalating privileges on the compromised system. To evade detection, the attackers used obfuscation techniques and fileless execution before collecting mailbox data and sensitive authentication information. In the final stage, they established remote command-and-control channels to exfiltrate collected sensitive data. Researchers also observed the use of specialized download tools such as Zimclient2 to establish more complex remote connections, as well as attempts to exfiltrate data through cloud services.
Administrators should immediately update Zimbra to version 10.1.20 or later to address the vulnerability. If an update cannot be applied immediately, they should consider uninstalling the zimbra-snmp package, disabling SNMP notifications, and restricting network access to SNMP and SMTP services to trusted hosts only. Administrators should also review system logs, particularly /var/log/zimbra.log, for unusual service restart activity, rotate all authentication credentials, and scan server directories for web shells that may have been deployed to maintain persistent access and reduce the risk of reinfection.
Source: https://thehackernews.com/2026/09/attackers-exploit-zimbra-flaw-to-deploy.html