
554/69 Thursday, October 8, 2026
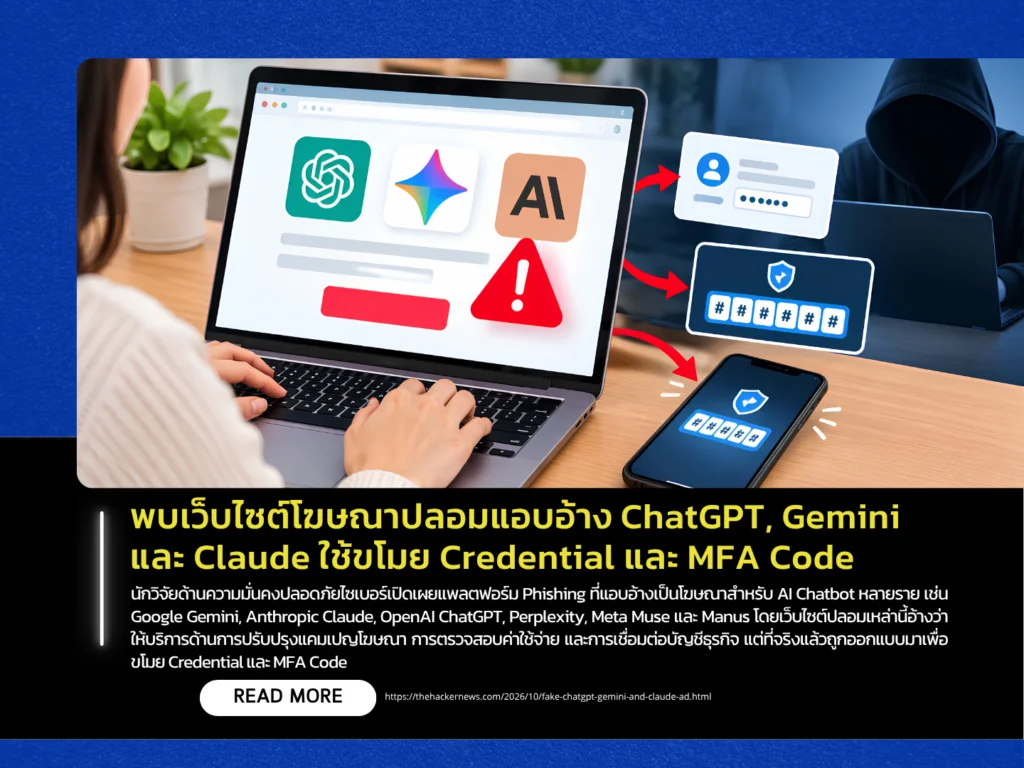
Cybersecurity researchers have disclosed a phishing platform impersonating advertising services associated with multiple AI chatbots, including Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus. The fake websites claim to provide services such as advertising campaign optimization, spending monitoring, and business account integration. In reality, they are designed to steal credentials and MFA codes through fake login windows using the Browser-in-the-Browser (BitB) technique. This method creates a simulated browser window inside the real browser, complete with a fake address bar displaying trusted-looking domains such as accounts.google.com or an Okta tenant.
Island stated that the “Connect” button on these fake websites serves as a key starting point for the attack. When users click it, the site opens a fake login window impersonating services such as Google, Meta, TikTok, and Okta to trick victims into entering their credentials. At the same time, the backend fingerprints the victim’s device, sends the collected information to an attacker-controlled endpoint, and allows the operator to select which MFA challenge should be displayed to the victim in real time. The attackers then use the stolen credentials to immediately attempt login to the legitimate account. Each impersonated AI brand uses tailored content and offers to appear more convincing. For example, the fake ChatGPT site claims to provide weekly Google Ads summaries, Gemini claims to support Manager Accounts and linked client accounts, Claude presents a dedicated advertising portal, Perplexity offers campaign planning and spending reviews, while Manus claims to provide private integration with Meta.
The report stated that victims are commonly directed to these websites through fraudulent emails impersonating trusted AI brands. All of the fake sites share common technologies such as Next.js and Socket.IO and communicate with the same endpoint. Researchers also found that the campaign is part of a broader phishing platform supporting additional fake sites themed around Google Ads refunds, payment confirmations, and job recruitment pages impersonating brands such as Tesla, Louis Vuitton, Nike, and Adecco. The primary targets of the fake AI advertising campaign are agency employees, media buyers, and Manager Account administrators, as advertising accounts with established histories can be abused to run attacker-controlled campaigns or resold. Organizations should therefore adopt phishing-resistant authentication, monitor changes to advertising account permissions, and carefully assess AI integrations before allowing them to access sensitive business accounts.
Source: https://thehackernews.com/2026/10/fake-chatgpt-gemini-and-claude-ad.html