
558/69 Friday, October 9, 2026
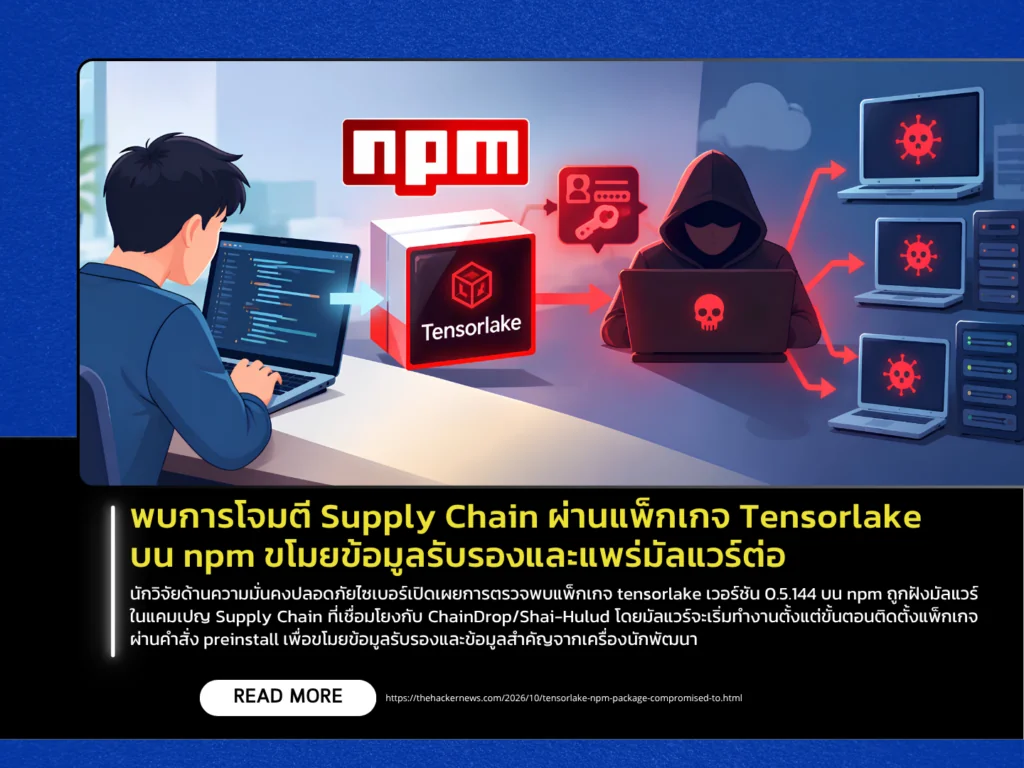
Cybersecurity researchers have disclosed that version 0.5.144 of the tensorlake package on npm was compromised with malware as part of a supply chain campaign linked to ChainDrop/Shai-Hulud. The malware executes during package installation through a preinstall script and is designed to steal credentials and sensitive information from developer systems, including npm and GitHub tokens, AWS credentials, Kubernetes and HashiCorp Vault credentials, SSH keys, .env files, and data associated with certain AI development tools. Following discovery of the incident, version 0.5.144 of the package was removed from npm.
The malware collects and exfiltrates data from infected systems and uses stolen npm tokens to modify and publish additional packages under victims’ accounts, allowing it to spread further through the software supply chain. Researchers also observed files being created in the .claude and .vscode directories so that malicious commands could be executed again when users opened projects through Claude Code or Visual Studio Code. In addition, the malware includes a mechanism that continuously monitors stolen GitHub tokens. Reports warn that revoking a GitHub token before removing this mechanism could trigger commands capable of deleting or damaging data on the affected system.
Developers who installed tensorlake@0.5.144 should treat any system on which the installation script executed as potentially compromised. They should review related dependencies, lockfiles, and build logs, stop using the affected version, and revert to a trusted release such as version 0.5.143 while conducting incident investigation and remediation. GitHub tokens should not be revoked before checking for and removing the gh-token-monitor mechanism, as doing so could trigger destructive commands. After the malware has been contained and removed, organizations should rotate any credentials that may have been exposed from a trusted system and review npm, GitHub, and cloud service accounts for unauthorized package publication or other suspicious activity.
Source: https://thehackernews.com/2026/10/tensorlake-npm-package-compromised-to.html